APT28 SOHO Router DNS Hijacking & Adversary-in-the-Middle Campaign
Defensive analysis of the NCSC, NSA and FBI advisory covering compromised edge devices, redirected authentication traffic and credential interception risk.
Exploit & target surface
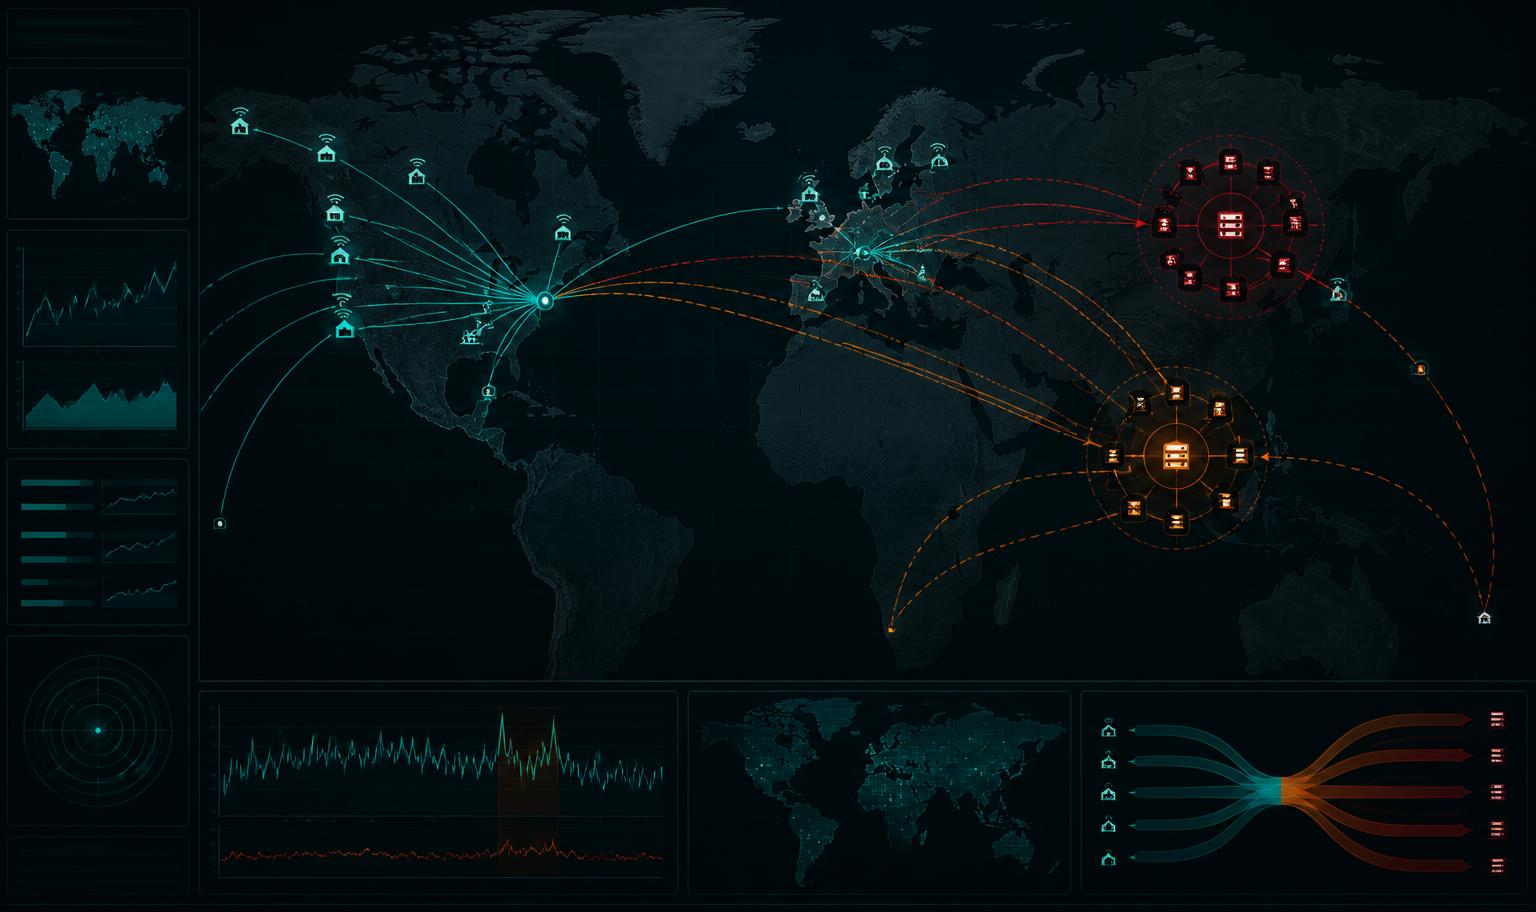
The observed tradecraft turns unmanaged edge equipment into a redirection layer. Exploitation risk is highest where vulnerable firmware, exposed administration and unchanged default controls overlap. Model names below are a partial targeting matrix; defenders should validate exact hardware revisions and supported firmware with the vendor advisory.
Legacy SOHO routing family
Dual-band consumer gateways
LTE and mobile broadband routers
Wireless dual-band routers
Legacy wireless N devices
Multi-antenna SOHO routers
Infrastructure cluster behavior
Cluster 01 // Redirect
Receives resolver traffic after DHCP or DNS settings are modified. VPS hosts may expose dnsmasq characteristics and rotate to reduce blocking durability; configuration changes are a stronger signal than a static version string.
Cluster 02 // Relay
Supports downstream interception and credential-harvest activity against mail and identity endpoints. Assess session tokens for potential compromise after confirmed redirection and consider precautionary revocation.
Infrastructure is volatile. Validate IP addresses against the latest official advisory feed before deploying blocks; stale indicators may be reassigned.
Indicators of compromise
Switch indicator groups, filter the list, and expand each entry for defensive context. Domains are defanged for safe handling.
Actionable mitigation checklist
Use the checklist as an initial response aid, then align actions with your incident-response process and the latest vendor and government guidance.
Priority defense controls
0 of 5 marked complete